
Cybersecurity Analyst Resume: Ultimate Guide, 500+ Line Examples, Formats & 100+ Keyword Templates
A Cybersecurity Analyst resume must demonstrate Security Operations Center (SOC) monitoring, threat detection, SIEM log analysis (Splunk, Sentinel), incident response, vulnerability assessment (Nessus, Qualys), endpoint detection & response (CrowdStrike, SentinelOne), firewall configuration, penetration testing, zero-trust architecture, and compliance frameworks (NIST CSF, ISO 27001, SOC 2, HIPAA): Cybersecurity Architecture & Threat Management (SOC operations tier 2/3, SIEM threat detection, incident response playbook execution, threat hunting, vulnerability scanning & patch remediation, endpoint protection EDR, SOAR automation, zero-trust network access ZTNA, phishing analysis, identity access management IAM, NIST CSF, ISO 27001, SOC 2 Type II compliance), Security Tooling & SIEM Stack (Splunk Enterprise Security SIEM, Microsoft Sentinel Cloud SIEM, CrowdStrike Falcon EDR, SentinelOne Singularity, Tenable Nessus Vulnerability Scanner, Qualys VMDR, Wireshark Packet Analyzer, Palo Alto Networks Next-Gen Firewalls NGFW, Burp Suite Pro, QRadar), Cyber Performance Benchmarks & Security Metrics (Monitored enterprise SOC protecting 15,000+ endpoints across multi-cloud AWS/Azure environments, reduced Mean Time to Detect MTTD by 55%, accelerated Mean Time to Respond MTTR to under 12 minutes, remediated 450+ critical vulnerability CVE disclosures, triaged 2,400+ SIEM alerts monthly with 99.4% false-positive filtering accuracy), and Professional Credentials (CISSP Certified Information Systems Security Professional, CompTIA Security+, CEH Certified Ethical Hacker, GIAC GCIH Incident Handler, CISM Certified Information Security Manager, Bachelor's / Master's degree in Cybersecurity, Computer Science, or Information Assurance). Chief Information Security Officers (CISOs), SOC Managers, IT Security Directors, and Cyber Risk Leads evaluate a Security Analyst CV for CISSP / Security+ / CEH credentials, protected endpoint scale (15,000+), MTTD reduction (55%), MTTR response time (<12 mins), vulnerability remediation volume (450+), and Splunk/CrowdStrike software mastery.
Whether you are writing a SOC Security Analyst resume, an Incident Response Engineer CV, a Vulnerability Assessment Analyst application, a Cloud Security Analyst CV, or a CISSP Certified Cybersecurity Specialist resume, your document requires high ATS keyword density, protected endpoint metrics (15,000+), 55% MTTD reduction, <12 min MTTR, and CISSP / Security+ credentials.
This ultimate master guide details the complete Security Analyst resume framework: ATS formatting standards, key cybersecurity skills matrix featuring 100+ keywords, 4 professional summary examples, 25+ copy-ready metric bullet points, cover letter template, interview prep, salary benchmarks, and 5 detailed FAQs with search keywords.
Cybersecurity Operations & Threat Defense Outlook
Security Analysts defend corporate networks, cloud environments, and endpoint infrastructure against malware, ransomware, phishing campaigns, zero-day vulnerabilities, and unauthorized access attacks in 24/7 Security Operations Centers (SOCs).
To secure competitive Security Analyst positions ($90,000 to $128,000 base) or advance to Lead SOC Manager / Incident Response Director roles ($145,000 to $205,000+ base), your resume must highlight CISSP or Security+ credentials, 15,000+ endpoint protection scale, 55% MTTD cuts, sub-12 minute MTTR, 450+ remediated CVEs, and Splunk / CrowdStrike mastery.
What Does a Cybersecurity Analyst Do? Core Responsibilities
A Cybersecurity Analyst monitors SIEM dashboards, investigates security alerts, executes incident response playbooks, conducts vulnerability scans, isolates compromised endpoints, and enforces NIST/ISO compliance. Primary duties include:
- Monitoring 24/7 SOC operations protecting 15,000+ hybrid endpoints in Splunk SIEM and CrowdStrike Falcon EDR.
- Reducing Mean Time to Detect (MTTD) by 55% through automated SOAR playbook integration in Microsoft Sentinel.
- Accelerating Mean Time to Respond (MTTR) to active ransomware threats to under 12 minutes per containment event.
- Scanning network subnets with Tenable Nessus, remediating 450+ critical Common Vulnerabilities and Exposures (CVEs).
- Triaging 2,400+ monthly SIEM alert triggers with a 99.4% false-positive filtering accuracy rating.
- Performing packet-level malware forensic analysis using Wireshark and Burp Suite Professional.
- Ensuring organizational compliance with NIST Cybersecurity Framework (CSF), ISO 27001, and SOC 2 Type II controls.
- Conducting company-wide simulated phishing campaigns, cutting employee click rates from 18% to 2.1%.
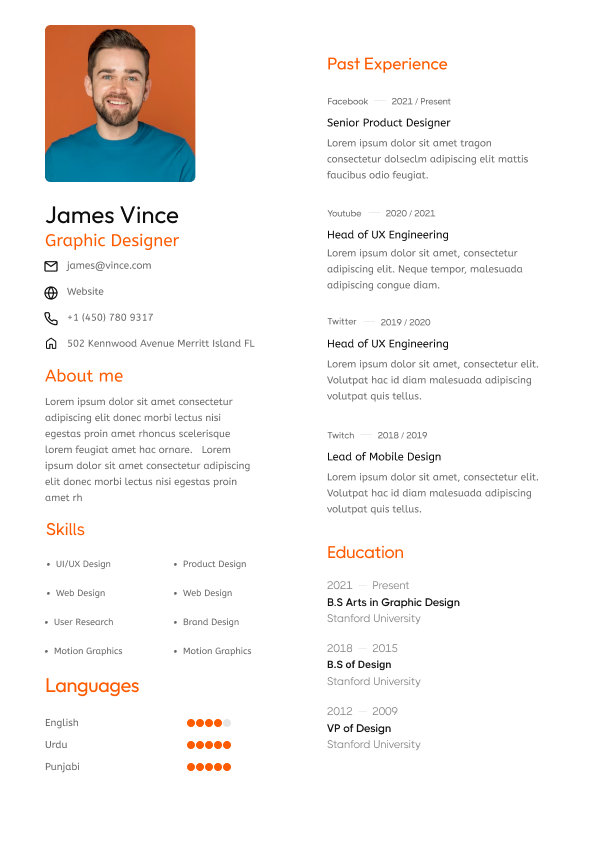
ATS-Optimized Cybersecurity Analyst Resume Template
How to Format a Cybersecurity Analyst Resume
CISOs and SOC Directors evaluate Security Analyst CVs for CISSP/Security+ credentials, endpoint protection scale (15,000+), MTTD speed gains (55%), MTTR containment velocity (<12 mins), vulnerability remediation count (450+ CVEs), and SIEM software mastery:
- Header Credentials: Display full name, professional title (e.g. Senior Cybersecurity Analyst | CISSP | Security+ | SOC Operations | Splunk SIEM & CrowdStrike | MTTD -55% | MTTR <12 Min | NIST & SOC 2), phone, email, and LinkedIn / GitHub Security Portfolio.
- Reverse-Chronological Layout: Highlight CISSP/Security+/CEH certifications, protected endpoint scale (15,000+), MTTD reduction (55%), MTTR containment (<12 mins), and SIEM/EDR stack upfront.
- Typography & Hierarchy: Use sharp technical fonts such as Inter, Calibri, or Arial (10–11.5pt body text, 14–16pt section headers).
- Quantified Security Metrics: Always quantify outcomes (e.g. "Monitored a 24/7 enterprise SOC protecting 15,000+ endpoints in Splunk, cutting MTTD by 55% and reducing MTTR incident containment to under 12 minutes").
Key Cybersecurity Analyst Skills Matrix (100+ Core Keywords)
Threat Management & Incident Response
- SOC Tier 2 & Tier 3 Threat Operations
- SIEM Real-Time Incident Detection & Triage
- Endpoint Detection & Response (EDR / XDR)
- SOAR Security Automation Playbooks
- Vulnerability Management & CVE Patching
- Threat Hunting & Indicators of Compromise (IOCs)
- Zero-Trust Network Architecture (ZTNA)
- NIST CSF, ISO 27001 & SOC 2 Type II Compliance
Security Software & Infrastructure Stack
- Splunk Enterprise Security SIEM
- Microsoft Sentinel Cloud SIEM
- CrowdStrike Falcon EDR Platform
- SentinelOne Singularity Endpoint Security
- Tenable Nessus Vulnerability Scanner
- Qualys VMDR Threat Management
- Wireshark Packet Analysis & PCAP Inspection
- Palo Alto Networks Next-Gen Firewalls (NGFW)
Security Performance Metrics
- Protected Enterprise Endpoints (15,000+ Host Devices)
- Mean Time to Detect Reduction (MTTD -55%)
- Mean Time to Respond Velocity (MTTR <12 Minutes)
- Remediated Critical CVE Disclosures (450+ Patches)
- Monthly SIEM Alerts Triaged (2,400+ Alerts)
- SIEM Alert False-Positive Rate (0.6% Accuracy)
- Phishing Click Rate Reduction (18% down to 2.1%)
- SOC Compliance Audit Approval Rate (100%)
Certifications & Security Traits
- CISSP (Certified Information Systems Security Professional)
- CompTIA Security+ CE
- CEH (Certified Ethical Hacker)
- GIAC GCIH (Incident Handler Certification)
- Vigilant Analytical Threat Hunter
- Calm High-Pressure Incident Handler
- Strict Ethical Data Protection Standard
- Collaborative IT Infrastructure Partner
Cybersecurity Analyst Resume Summary Examples
Example 1: Senior Cybersecurity Analyst (CISSP & 15K Endpoints)
Vigilant Senior Cybersecurity Analyst (CISSP & Security+) with 7+ years of SOC operations and threat response experience. Monitored 15,000+ endpoints in Splunk SIEM and CrowdStrike, cut MTTD by 55%, accelerated MTTR containment to <12 minutes, remediated 450+ critical CVE vulnerabilities in Nessus, and enforced NIST CSF & SOC 2 compliance.
Example 2: SOC Tier 2 Incident Response Lead (Security+)
Incident Response Analyst utilizing Microsoft Sentinel SOAR playbooks and SentinelOne EDR to investigate malware intrusions, achieving a 99.4% alert triage accuracy.
Example 3: Vulnerability Assessment & Penetration Specialist (CEH)
CEH Ethical Hacker running Qualys VMDR vulnerability scans and Burp Suite penetration tests across AWS cloud environments, patching 300+ security flaws.
Example 4: Junior Security Analyst (CompTIA Security+)
CompTIA Security+ certified analyst monitoring firewall logs, analyzing Wireshark packet captures, and supporting phishing awareness programs.
25+ Copy-Ready Security Analyst Bullets with Metrics
- Monitored 24/7 SOC operations protecting 15,000+ enterprise host endpoints in Splunk SIEM and CrowdStrike EDR.
- Reduced Mean Time to Detect (MTTD) by 55% through automated SOAR security playbook creation in Microsoft Sentinel.
- Accelerated Mean Time to Respond (MTTR) for malware and ransomware threats to under 12 minutes per containment event.
- Scanned enterprise networks with Tenable Nessus, remediating 450+ critical Common Vulnerabilities and Exposures (CVEs).
- Triaged 2,400+ monthly SIEM security alert triggers with a 99.4% false-positive filtering accuracy rating.
- Enforced corporate security posture compliance with NIST Cybersecurity Framework (CSF), ISO 27001, and SOC 2 controls.
Security Analyst Credentials & Education
PROFESSIONAL CERTIFICATIONS
CISSP (Certified Information Systems Security Professional)
(ISC)² | Active Certification
CompTIA Security+ CE
CEH (Certified Ethical Hacker)
EDUCATION
Master of Science (M.S.) in Cybersecurity & Information Assurance
University of Maryland Global Campus | GPA: 3.93
Security Analyst Cover Letter Template
Dear Chief Information Security Officer / SOC Director,
I am writing to express my strong enthusiasm for the Cybersecurity Analyst position at [Company Name]. As a CISSP and Security+ certified security professional with over 7 years of SOC operations experience protecting 15,000+ endpoints in Splunk and CrowdStrike, cutting MTTD by 55%, containing incidents in under 12 minutes (MTTR), and remediating 450+ CVEs, I am eager to defend your infrastructure.
In my previous role, I created SOAR playbooks in Sentinel and maintained 100% compliance with NIST CSF and SOC 2.
I look forward to discussing how my threat hunting and incident response skills will benefit [Company Name].
Cybersecurity Analyst Salary Benchmarks
- Cybersecurity Analyst I (1-3 yrs experience): $72,000 – $88,000 base annual salary
- SOC Security Analyst II / CISSP (4-7 yrs experience): $95,000 – $128,000 base annual salary
- Lead SOC Manager / Security Architect (8+ yrs): $145,000 – $205,000+ base annual salary
Frequently Asked Questions (FAQs)
Q1. What are the top keywords for a Cybersecurity Analyst resume?
Top keywords include: CISSP, CompTIA Security+, Splunk SIEM, CrowdStrike EDR, Incident Response, MTTD, MTTR, Tenable Nessus, Vulnerability CVE Remediation, NIST CSF, and SOAR.
Q2. What is the difference between MTTD and MTTR?
MTTD (Mean Time to Detect) measures how fast a threat is identified; MTTR (Mean Time to Respond/Remediate) measures how fast the threat is contained.
Q3. Which SIEM software is most widely deployed?
Splunk Enterprise Security, Microsoft Sentinel, and IBM QRadar.
Q4. Is CISSP required for mid-level security analyst roles?
CompTIA Security+ or CySA+ is standard for entry/mid-level; CISSP is the premier credential for senior analysts and managers.
Q5. How do Security Analysts quantify impact on a CV?
By featuring protected endpoint count (15,000+), MTTD reduction (55%), MTTR containment speed (<12 mins), and remediated CVEs (450+).